
Rockstar Strategies for De-risking Your Software Supply Chain

Webinar
Today’s cyber threat landscape is rife with sophisticated attacks aimed at the software supply chain. Gartner estimates that by 2025, 45% of organizations will have experienced one. This is largely due to the rising proliferation of OSS components in modern applications, which introduces an increasing number of vulnerabilities. In the wake of high-profile breaches such as Log4j and SolarWinds, software-producing organizations are under increased regulatory pressure to ensure the integrity of their applications for customers and users.
This webinar offers expert guidance on approaching software supply chain security with a look at the people, processes, and tools needed across the software development lifecycle. You’ll learn about the importance of Supply chain Levels for Software Artifacts (SLSA) compliance during the build process, Software Bills of Material (SBOMs), and the capabilities you’ll need to have in place in order to remediate zero-day vulnerabilities and license compliance issues.
Why You Should Join:
- Understand the evolving security threat landscape around software supply chains and the security & compliance implications for software-producing organizations
- Understand the Supply chain Levels for Software Artifacts (SLSA) framework and how it is instrumental in evaluating the trustworthiness of software artifacts during and after the build process
- Learn about the Software Bill of Materials (SBOM) and how it is instrumental for governing open source software (OSS) components and for complying with Executive Order 14028.
Speakers
-
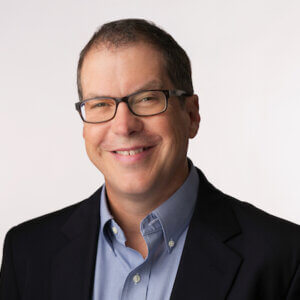
Scott Bekker Webinar Moderator ActualTech Media
-

Sean Roth Director, Product Marketing Harness
-
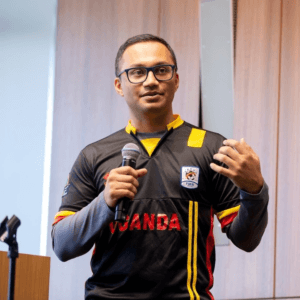
Chinmay Gaikwad Director, Product Marketing Harness